Managed-site candidate
Qualify the private-site identity and approval workflow first.
Implementation candidate · managed-site validation required
OpenRoaming can connect compatible identities and participating Wi-Fi operators. Our first release establishes controlled connectivity on supported HotSpotVU sites before external federation qualification.
Qualify the private-site identity and approval workflow first.
Validate identity acceptance and network behavior in both directions.
Publish coverage only after validation and service agreements.
External federation remains a qualification and partnership milestone.
EAP-TLS provides certificate-based Wi-Fi authentication. Passpoint can provide supported discovery and network selection. RADIUS and protected federation transport connect authentication infrastructure.
FIDO Device Onboard can complement initial connectivity with ownership transfer and operational provisioning. It is not a replacement for Wi-Fi admission or a guarantee of ongoing Internet service.
An access provider admits approved external identities onto its network. An identity provider supplies or represents credentials that other participating networks can authenticate.
Operating HotSpotVU hotspots alone does not make our enrolled devices eligible on every external network. The identity role, partner acceptance, supported platforms, policies, and commercial terms must be validated.
Manufacturers still need identity lifecycle management and fleet support. Businesses still need appropriate admission and capacity controls. Usage billing and operator compensation need measurement and commercial arrangements.
A visited network controls local packet forwarding and enforcement. HotSpotVU cannot promise that every third-party operator will apply a proprietary policy or supply the same usage and status data.
First qualify certificate authentication and the owner-approval flow at managed sites. Then test external identities on a HotSpotVU test network and our test identities on an agreed partner network.
Publish validated coverage and policy/accounting capabilities only after those tests and agreements. OpenRoaming certification, federation membership, and global service availability are not implied by this software implementation.
WBA’s September 2026 IoT announcement describes initial connectivity and device onboarding. That result does not establish HotSpotVU commercial roaming availability or persistent metered service.
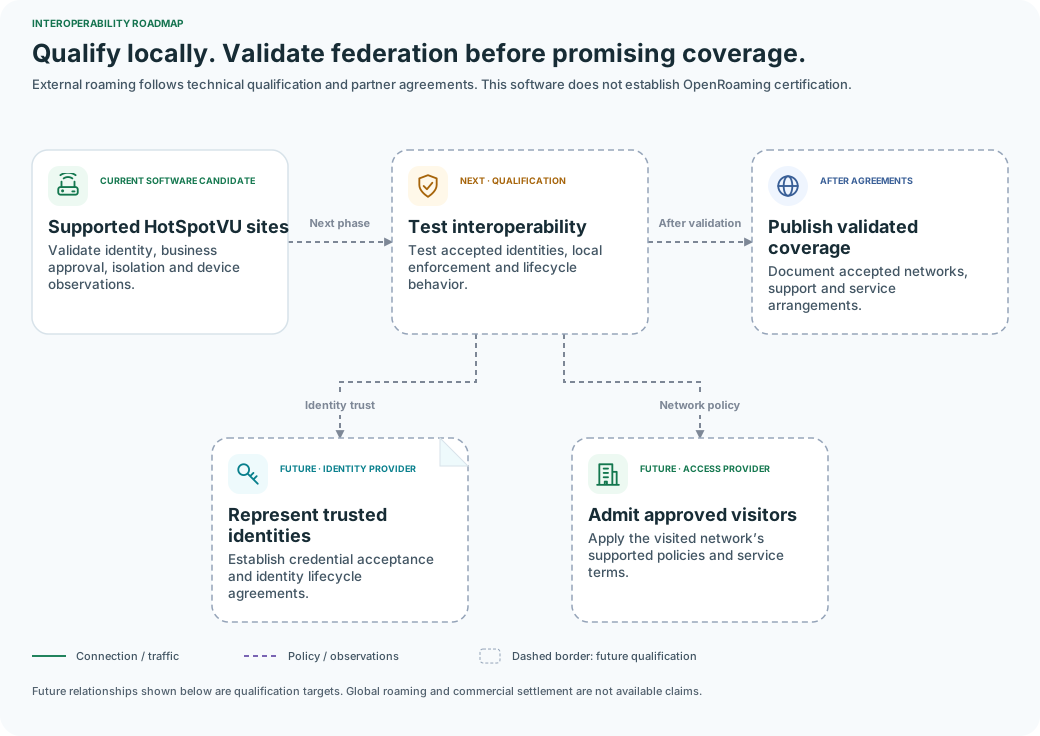
Validate identity, business approval, isolation and device observations.
Test accepted identities, local enforcement and lifecycle behavior.
Document accepted networks, support and service arrangements.
Establish credential acceptance and identity lifecycle agreements.
Apply the visited network’s supported policies and service terms.
Read the WBA 2026 trials overview and the WBA and FIDO onboarding framework for the federation and onboarding work behind this direction.