Identity
EAP-TLS establishes which enrolled credential is present.
Implementation candidate · managed-site validation required
The service links an enrolled device to a local network decision while preserving separate manufacturer, provider, and business responsibilities.
EAP-TLS establishes which enrolled credential is present.
The site decides whether that device can use its network.
Recent measurements describe connectivity, not application health.
Target supported hardware and an enabled site. Your application retains its own health and recovery responsibilities.
Each device has a stable registry identity and its own certificate. The private key stays with the device or its protected manufacturing environment. MAC addresses and browser descriptions are not authoritative manufacturer identity.
Wi-Fi endpoint credentials, satellite infrastructure credentials, and gateway cloud-management credentials serve different roles and must not be reused interchangeably.
Device application traffic travels through the local network and its upstream Internet connection. Device status and policy events travel over authenticated management paths.
The partner API manages enrollment, permissions, and observations; it is not a tunnel that supplies Internet connectivity where no upstream service exists.
IoT clients use an isolated network with independent capacity allocation. Satellite backhaul and management use restricted infrastructure access. Existing guest service remains separate.
Network features are disabled by default and enabled per qualified site. Established sessions can retain installed policy within its validity period during control-service interruption; new authentication fails closed and retries.
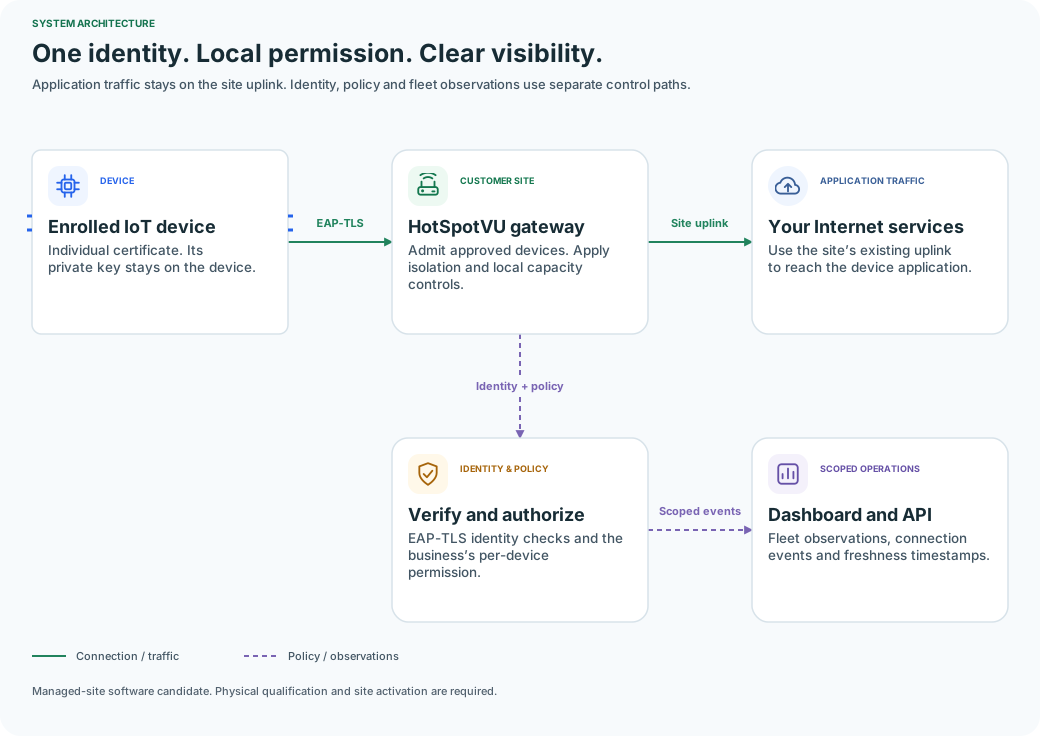
Individual certificate. Its private key stays on the device.
Admit approved devices. Apply isolation and local capacity controls.
Use the site’s existing uplink to reach the device application.
EAP-TLS identity checks and the business’s per-device permission.
Fleet observations, connection events and freshness timestamps.